Critical PHP Vulnerabilities in October 2026: How Memory Management Flaws Threaten Web Servers
By Suhib Jarrah | Principal Cyber Security Engineer
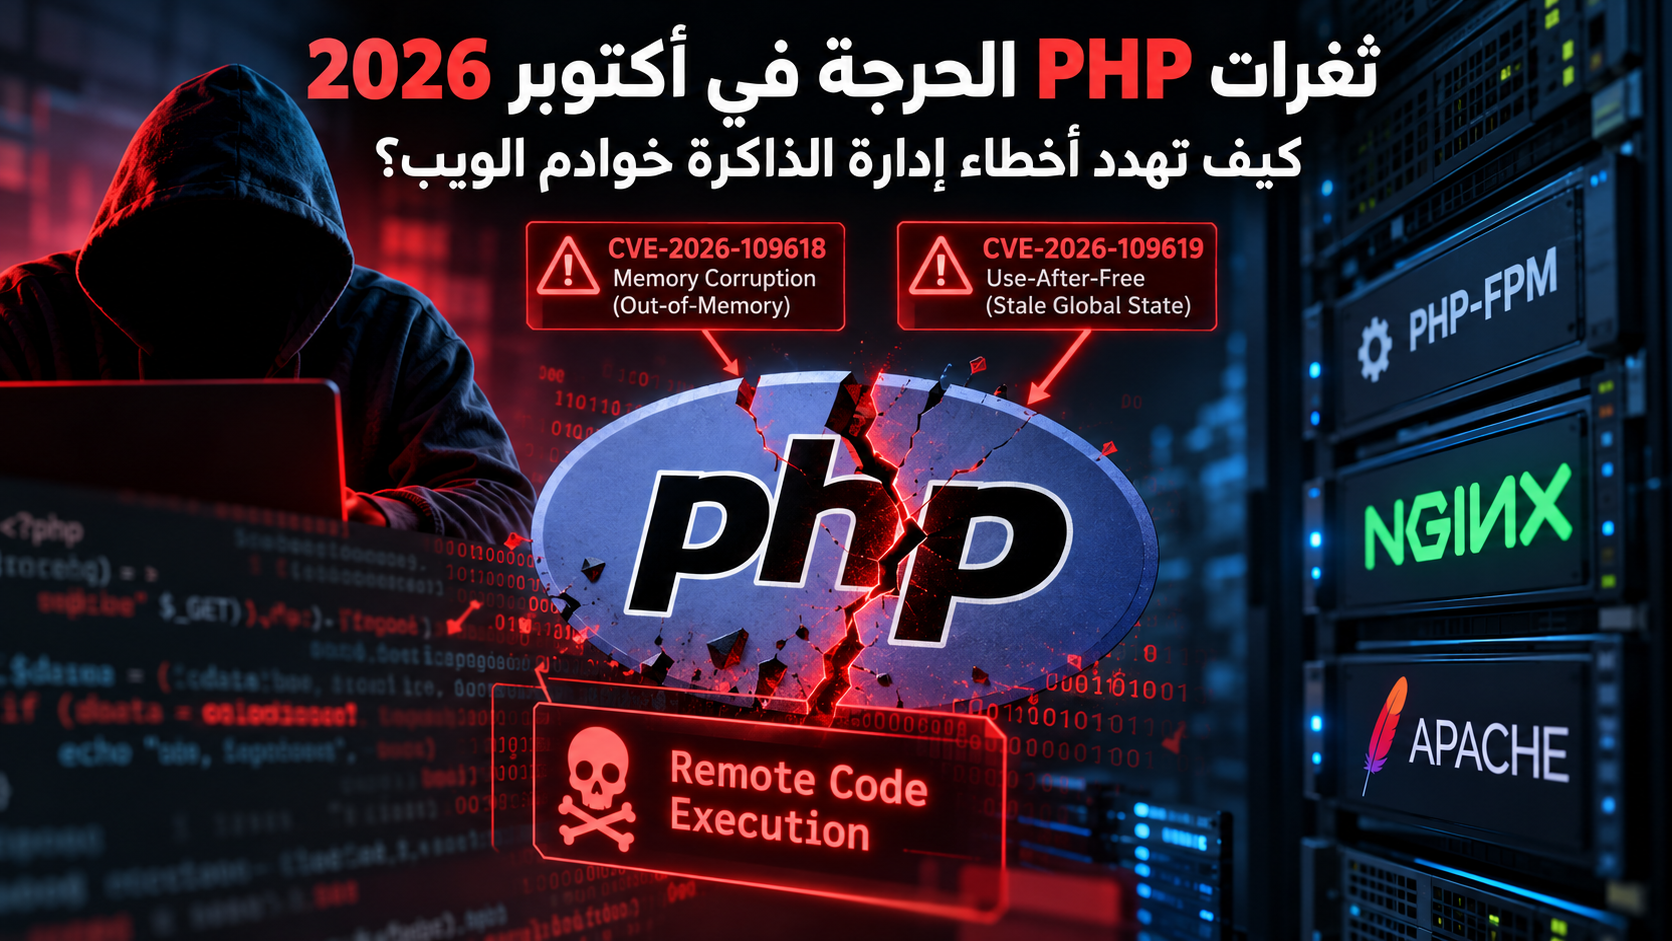
On October 21, 2026, the PHP development team released emergency security updates addressing two critical vulnerabilities in the PHP runtime, identified as CVE-2026-109618 and CVE-2026-109619.
Both vulnerabilities received a CVSS v4.0 score of 9.2 and could, under certain conditions, allow unauthenticated attackers to achieve remote code execution (RCE) or access sensitive process memory.
What makes these vulnerabilities particularly concerning is that they affect the underlying PHP runtime rather than a specific application or framework.
Even a carefully developed application that follows secure coding standards may remain vulnerable if it runs on an affected PHP version.
The disclosure prompted urgent warnings from cybersecurity authorities, including the United Kingdom's National Cyber Security Centre (NCSC), the European Union Agency for Cybersecurity (ENISA), and CERT-EU.
These vulnerabilities demonstrate an important principle in cybersecurity architecture: Application security cannot be separated from the security of the infrastructure and runtime environment supporting it.
1. Why Are PHP Runtime Vulnerabilities So Dangerous?
PHP is widely used to power dynamic websites, content management systems, enterprise portals, e-commerce platforms, and custom web applications.
When a user requests a PHP-powered web page, the web server forwards the request to the PHP runtime, which processes the necessary application logic and returns a response.
Common PHP deployment architectures include:
Nginx with PHP-FPM
Apache with mod_php
PHP-CGI
LiteSpeed
FrankenPHP
Although these configurations differ in how they handle web requests and PHP processes, they may share vulnerable components of the PHP runtime.
Consequently, a security flaw in the PHP engine can affect multiple applications and deployment architectures simultaneously.
Unlike a vulnerability in a single plugin or application component, a runtime-level vulnerability potentially exposes every application relying on the affected PHP version.
Using Laravel, WordPress, Drupal, Joomla, or a custom-built PHP application does not automatically eliminate this risk.
2. CVE-2026-109618: Memory Corruption During Out-of-Memory Handling
Vulnerability ID: CVE-2026-109618
Technical classification: Out-of-Memory Memory Corruption
Severity: Critical
CVSS v4.0 score: 9.2
The first vulnerability affects how PHP handles memory allocation failures during request processing.
Understanding the Technical Problem
PHP relies on internal memory management mechanisms to allocate, track, and release memory while executing application code.
One commonly used configuration directive is:
memory_limit
This setting controls the maximum amount of memory a PHP script is permitted to allocate.
When PHP reaches a memory allocation limit, the engine may interrupt execution and initiate error-handling and resource-cleanup procedures.
However, CVE-2026-109618 arises when out-of-memory handling interrupts PHP while certain internal request structures are only partially initialized.
During cleanup, the runtime may incorrectly treat those incomplete structures as valid data.
This can lead to memory corruption and, under exploitable conditions, unauthorized code execution.
Why Is This Significant?
The vulnerability occurs within PHP's internal request-processing lifecycle.
An attacker may be able to trigger the vulnerable condition through specially crafted input, depending on the affected environment and available attack surface.
Importantly, the underlying flaw exists below the application layer.
As a result, traditional secure coding practices cannot independently correct the vulnerability.
Even applications that properly validate input, use parameterized SQL statements, and follow secure software development practices still depend on the integrity of their PHP runtime.
3. CVE-2026-109619: Stale Global State and Use-After-Free
Vulnerability ID: CVE-2026-109619
Technical classification: Stale Global State / Use-After-Free
Severity: Critical
CVSS v4.0 score: 9.2
The second vulnerability concerns the lifecycle of internal request state and memory references in PHP.
What Is Use-After-Free?
In memory-managed software, data is allocated in memory while it is needed and released when it is no longer required.
A use-after-free vulnerability occurs when a program attempts to access a memory location after that memory has already been released.
Such errors can produce unpredictable behavior, crashes, sensitive information exposure, or, in some cases, code execution.
In CVE-2026-109619, request-owned internal state may survive after the memory supporting it has been freed.
A later request processed by the same PHP worker may access this stale state before normal initialization resets it.
Potential Security Consequences
Depending on execution conditions and memory layout, the vulnerability may enable an attacker to manipulate program behavior or access sensitive data.
However, the existence of a use-after-free vulnerability does not mean every deployment is equally exploitable.
Actual exploitation depends on the runtime configuration, process lifecycle, reachable input paths, and other environmental factors.
Nevertheless, such flaws are especially concerning in server-side runtimes responsible for processing untrusted network requests.
4. How Are These Vulnerabilities Different from SQL Injection and XSS?
Most developers are familiar with application-level vulnerabilities such as SQL Injection and Cross-Site Scripting (XSS).
SQL Injection typically occurs when an application constructs database queries using improperly handled input.
XSS generally arises when untrusted content is rendered in a browser without appropriate contextual encoding or sanitization.
In both cases, the vulnerability usually originates from how the application processes data.
The newly disclosed PHP vulnerabilities are fundamentally different.
They originate within the language runtime itself.
This distinction is crucial.
A developer may correctly implement:
Input validation
Output encoding
Parameterized SQL queries
Secure session management
Authentication and authorization controls
Yet the application may remain exposed if its underlying PHP runtime contains exploitable memory management flaws.
Secure application development and secure runtime management are complementary responsibilities, not interchangeable controls.
5. Are Nginx, Apache, and PHP-FPM Environments Affected?
The PHP runtime can operate through several server architectures.
Understanding these architectures is essential when assessing exposure.
Nginx with PHP-FPM
In this architecture, Nginx handles incoming HTTP requests and forwards PHP execution requests to PHP-FPM using FastCGI.
PHP-FPM manages PHP worker processes that execute application code.
If the PHP-FPM version is affected, using Nginx does not eliminate the runtime vulnerability.
The vulnerable code remains inside PHP itself.
Apache with mod_php
Apache can execute PHP through its mod_php module.
The PHP security advisory identified this deployment model as particularly concerning for the disclosed issues, including exploitation paths that may be reachable before normal application code executes.
Other Runtime Configurations
Organizations should also assess PHP-CGI, LiteSpeed, FrankenPHP, and other products embedding the PHP runtime.
The actual level of exposure depends on how the environment processes requests and whether vulnerable functionality is reachable.
A web server's name alone is not sufficient to determine whether an application is protected. The PHP runtime version and its configuration must be verified.
6. Affected PHP Versions and Security Updates
On October 21, 2026, the PHP development team released security updates addressing CVE-2026-109618 and CVE-2026-109619.
The corrected releases are:
| PHP Branch | Security-Fixed Version |
|---|---|
| PHP 8.2 | 8.2.35 |
| PHP 8.3 | 8.3.36 |
| PHP 8.4 | 8.4.27 |
| PHP 8.5 | 8.5.12 |
Earlier upstream releases within these branches require updating.
PHP 8.1 and older branches have reached end of life under the official PHP release lifecycle and should be migrated to supported versions.
Some operating-system vendors may provide backported security patches. Administrators must verify those protections through the relevant vendor's security advisories rather than relying solely on the upstream version number.
An Important Warning About PHP Version Checks
The following command:
php -v
typically displays the PHP Command-Line Interface (CLI) version.
It does not necessarily identify the PHP runtime serving a particular website.
For example, a server might use PHP 8.4 as its default CLI version while an individual website runs PHP 8.2 through PHP-FPM.
In multi-version hosting environments, administrators must verify each site's actual PHP-FPM pool, runtime configuration, and installed package versions.
Failing to distinguish between CLI and web-serving PHP versions can create a false sense of security.
7. Additional PHP Security Advisory: October 23, 2026
On October 23, 2026, the PHP security team published an additional advisory concerning:
CVE-2026-115560
This issue involves an unusual interaction between PHP session configuration and the Session Upload Progress functionality.
According to the advisory, exposure requires specific application behavior involving changes to the session serialization handler before a session starts.
Consequently, not all PHP applications are affected by this vulnerability under normal configurations.
The October 21 security releases did not include a fix for this additional issue.
Pending an appropriate fix, the PHP security team recommended disabling session upload progress where practical.
The relevant configuration directive is:
session.upload_progress.enabled=0
Administrators should assess whether their applications require this feature before changing the setting.
Any configuration changes must be applied to the relevant PHP runtime and followed by appropriate service reloads or restarts.
This vulnerability should be evaluated separately from CVE-2026-109618 and CVE-2026-109619 because its exploitation conditions and exposure characteristics differ.
8. How Can Administrators Determine Whether Their Servers Are Vulnerable?
Effective vulnerability assessment begins with accurate asset inventory.
Organizations should identify every web application, service, and embedded product that relies on PHP.
The next step is to establish the actual runtime version used by each application.
On Debian-based and Ubuntu-based systems, administrators can inspect installed packages using commands such as:
apt-cache policy php8.4-fpm
They can also inspect CLI versions with:
php -v
However, these commands alone are not sufficient for comprehensive verification.
The assessment should include:
Active PHP-FPM services and process versions
Website-specific PHP-FPM pools
Web server FastCGI configurations
Installed runtime packages and extensions
Vendor-provided security patches
Application dependencies and compatibility requirements
A server may host several PHP versions simultaneously.
Updating one branch does not automatically protect applications still running on another affected branch.
This is why accurate asset inventory and software version tracking are essential components of vulnerability management.
9. Is Updating PHP Enough to Eliminate the Risk?
For CVE-2026-109618 and CVE-2026-109619, installing a security-fixed PHP release is the primary remediation measure.
The PHP development team explicitly warned that there are no complete mitigations that can reliably replace patching.
However, administrators must verify that the updated runtime is actually being used by the affected applications.
They should also confirm that outdated worker processes have been replaced and that application functionality remains intact.
Important post-update checks include:
Website availability and HTTP responses
Authentication and authorization functions
Database connectivity
File upload operations
Administrative interfaces
Application logs and runtime errors
A successful package installation does not automatically prove that all websites are running the patched version.
Furthermore, patching prevents exposure to the specific corrected flaws going forward, but it does not establish whether a system was compromised before remediation.
If exploitation is suspected, organizations should conduct an incident investigation.
Such an investigation may include reviewing web access logs, PHP-FPM logs, abnormal processes, unexpected filesystem changes, suspicious accounts, and unusual outbound connections.
10. Recommended Security Measures for Organizations
10.1 Prioritize Security Updates
Internet-facing PHP services should receive the highest remediation priority.
Updates should be obtained through official PHP distribution channels or trusted operating-system and hosting-provider repositories.
10.2 Audit Every Installed PHP Version
Administrators should determine which applications use each installed PHP version.
In multi-tenant environments, separate PHP-FPM pools may run different versions on the same server.
Each active runtime must be evaluated independently.
10.3 Reduce the Attack Surface
Organizations should disable unnecessary services, restrict administrative interfaces, and limit network exposure wherever possible.
These measures reduce opportunities for exploitation but do not replace runtime security fixes.
10.4 Review File Upload and Session Configurations
Applications using file uploads or advanced session functionality warrant additional configuration reviews.
Session Upload Progress should be assessed in light of the October 23 advisory.
Changes should be tested carefully to avoid breaking legitimate application workflows.
10.5 Apply the Principle of Least Privilege
Web applications should execute under accounts with only the permissions required for their operations.
Database permissions, filesystem access, and service privileges should be restricted accordingly.
Although this approach does not prevent exploitation of every runtime flaw, it can reduce the consequences of a successful compromise.
10.6 Strengthen Logging and Monitoring
Security teams should monitor web server logs, PHP-FPM logs, authentication activity, filesystem changes, and outbound network traffic.
A lack of visible HTTP errors should not be interpreted as proof that exploitation has not occurred.
10.7 Establish Reliable Patch Management
Organizations should maintain tested backup and recovery procedures, compatibility testing environments, and documented update workflows.
Coordination between cybersecurity, infrastructure, and application development teams is essential.
A disciplined patch management process improves remediation speed while reducing operational disruption.
11. The Role of Zero Trust and Defense in Depth
These vulnerabilities highlight why cybersecurity cannot rely exclusively on secure application code.
Even well-designed applications may be exposed through weaknesses in operating systems, programming runtimes, third-party libraries, or supporting infrastructure.
A defense-in-depth architecture should therefore incorporate:
Runtime and operating-system patch management
Application and service isolation
Identity and access management
Least-privilege execution
Network segmentation
Continuous security monitoring
Vulnerability management
Incident response capabilities
These controls also align with Zero Trust principles, which emphasize minimizing implicit trust and continuously evaluating access.
However, Zero Trust does not replace security patches.
Its primary contribution in this context is helping reduce the potential impact and lateral movement associated with a successful compromise.
12. Key Cybersecurity Lessons from the October 2026 PHP Vulnerabilities
The October 2026 disclosures provide several important lessons for security architects, system administrators, and software development teams.
First, vulnerabilities in foundational software components can affect many otherwise unrelated applications.
Second, secure coding practices cannot compensate for unpatched vulnerabilities in the underlying runtime.
Third, security validation must examine the runtime actually serving production traffic, not merely the default version installed on the server.
Fourth, an organization's dependency on software repositories and hosting providers introduces operational risks related to patch availability and delivery speed.
Finally, vulnerability remediation requires more than installing an update. It also requires verification, monitoring, compatibility testing, and investigation where compromise is suspected.
These lessons reinforce the importance of treating infrastructure, runtime environments, and applications as interconnected components of a single security architecture.
Conclusion: A Secure Application Can Still Run on an Insecure Runtime
The critical PHP vulnerabilities disclosed in October 2026 demonstrate a fundamental cybersecurity principle:
The security of an application depends not only on its code but also on the integrity of the platform executing it.
Even applications developed according to recognized secure coding standards can face serious threats when their underlying runtimes contain exploitable memory management vulnerabilities.
Organizations must therefore combine secure development practices with systematic patch management, infrastructure hardening, access controls, monitoring, and incident response.
The ultimate objective is not simply to maintain functional applications but to build resilient systems capable of identifying, reducing, and responding to security risks across every layer of the technology stack.
Cybersecurity maturity is measured not only by the absence of known application flaws, but by an organization's ability to manage risk throughout its entire technical infrastructure.
References
Suhib Jarrah
Principal Cyber Security Engineer
https://suhibjarrah.com