By Eng. Suhib Jarrah | Principal Cyber Security Engineer
In a world increasingly dependent on digital communications, cloud services, and online applications, protecting devices and servers alone is no longer sufficient to ensure information security. Securing communication channels between users and systems has become one of the most important challenges in cybersecurity.
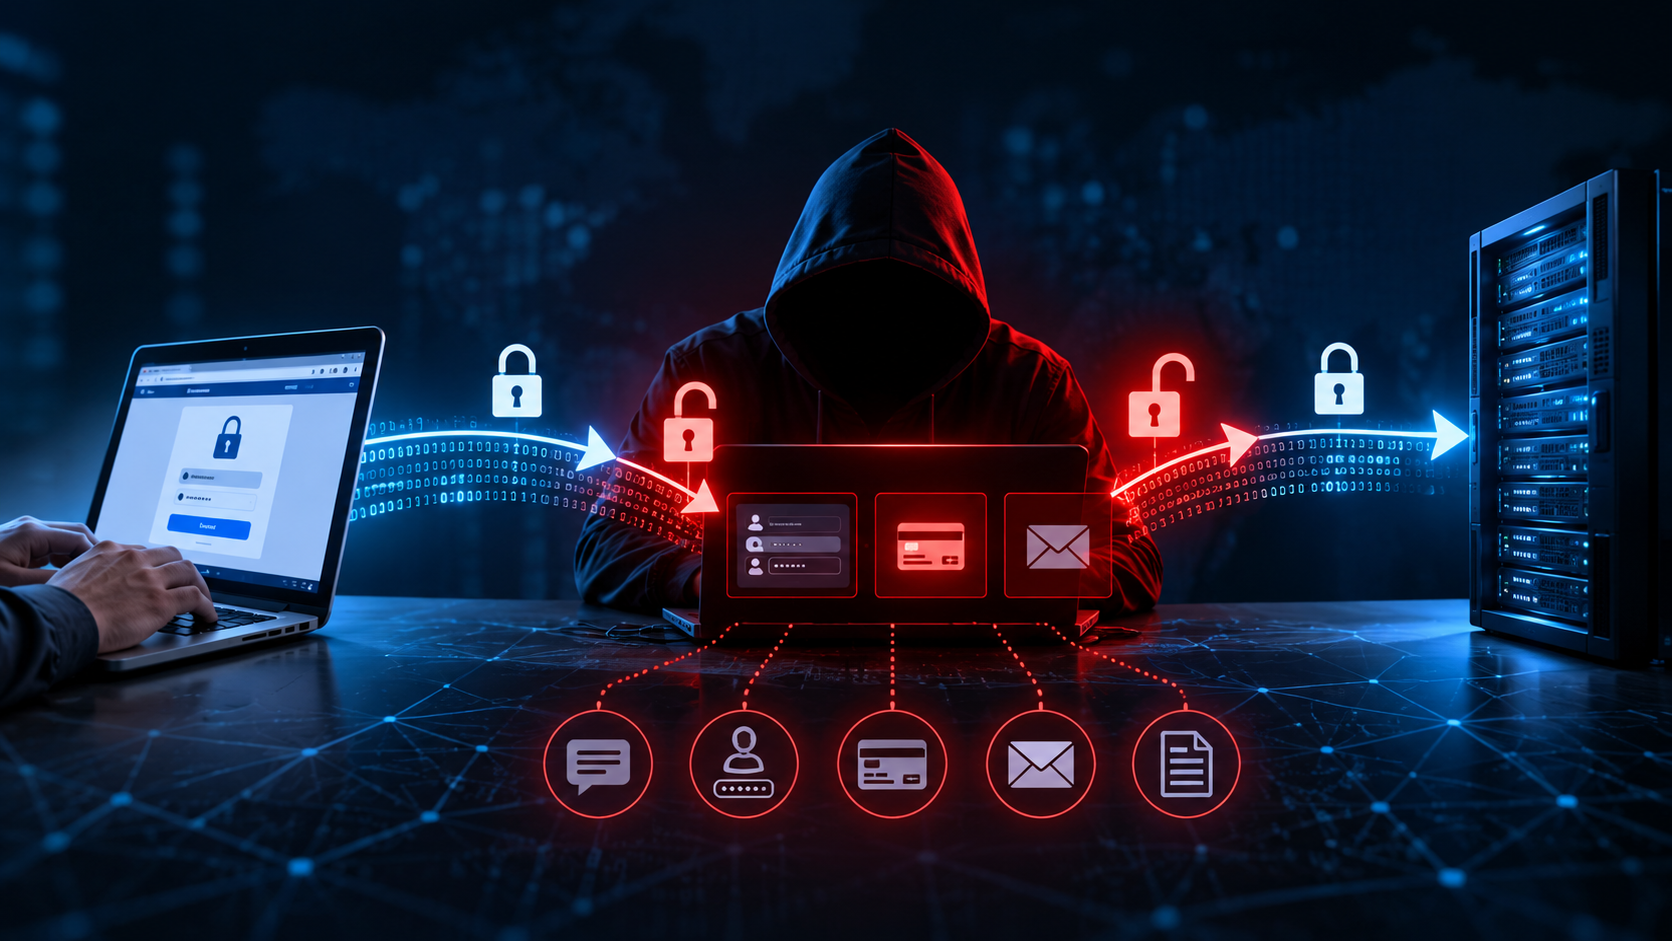
Man-in-the-Middle (MITM) attacks are serious threats to the confidentiality and integrity of digital communications. In these attacks, an adversary positions themselves between two communicating parties to intercept, monitor, or manipulate transmitted data without the knowledge of one or both parties.
What Are Man-in-the-Middle Attacks?
MITM attacks occur when an attacker gains the ability to intercept communications between a user's device and a server, or between two systems exchanging information.
Under normal circumstances, data travels through a communication channel between the intended parties. In an attack scenario, the adversary attempts to redirect network traffic through a device or system under their control.
A successful attack may expose sensitive information, alter transmitted content, or redirect users to fraudulent services.
However, intercepting network traffic does not necessarily mean that its contents can be read. Modern encryption and proper server identity verification provide important protection against these attacks.
Common Types of MITM Attacks
1. ARP Spoofing
ARP spoofing exploits the mechanism used to associate IP addresses with MAC addresses within local area networks.
An attacker attempts to send misleading ARP information, causing network devices to associate the default gateway's IP address with the attacker's MAC address. This may redirect part of the network traffic through the attacker's device.
This attack is particularly relevant to local networks that lack appropriate controls against address spoofing.
2. DNS Spoofing
In this scenario, an attacker attempts to manipulate DNS responses or redirect users to incorrect IP addresses.
This may cause a user to visit a fraudulent website resembling a legitimate banking service or login portal, potentially exposing authentication credentials.
Technologies such as DNSSEC help verify the integrity of DNS information when properly implemented, while HTTPS and certificate validation provide an independent layer of website identity protection.
3. Evil Twin Wi-Fi Attacks
An attacker creates a wireless access point using a name identical or similar to that of a trusted Wi-Fi network to encourage users to connect.
Once connected, an attacker may be able to observe certain network communications or attempt to redirect users to phishing websites.
Risks increase when users connect through unencrypted networks or ignore security certificate warnings.
4. SSL Stripping
SSL stripping targets situations in which an attacker can force or trick a user into communicating over an unencrypted HTTP connection instead of HTTPS.
Proper HTTPS deployment, combined with HTTP Strict Transport Security (HSTS) and modern browser security mechanisms, significantly reduces opportunities for this type of attack.
5. Session Hijacking
Attackers may target session tokens used by applications to maintain authenticated user sessions.
If an attacker obtains a valid session token, they may be able to impersonate the authenticated user, depending on the application's security controls and session protection mechanisms.
Multi-factor authentication alone may not always prevent the misuse of an already authenticated session.
MITM vs. Man-in-the-Browser: What Is the Difference?
Although both attacks may have similar objectives, important technical differences exist between them.
MITM attacks primarily focus on intercepting communication between endpoints. In contrast, a Man-in-the-Browser (MitB) attack involves manipulating the browser itself, often through malicious software or a compromised browser extension.
MitB attacks may manipulate information before encryption or after decryption within the browser. Consequently, they may succeed in scenarios where network interception alone cannot bypass HTTPS protection.
Can MITM Attacks Succeed Despite HTTPS?
The answer depends on the nature of the attack.
When an application uses modern TLS protocols with proper certificate validation, an attacker intercepting network traffic generally cannot read or modify encrypted content without detection.
However, risks may arise from weak TLS configurations, ignored certificate warnings, the installation of untrusted root certificates, or a compromise of either communication endpoint.
Therefore, HTTPS is a fundamental security measure, but it does not replace endpoint security, application protection, or effective digital trust management.
How Can MITM Attacks Be Detected?
Security teams rely on multiple indicators and detection mechanisms, including:
- Monitoring unexpected changes in network ARP tables.
- Detecting conflicting MAC addresses or unusual IP-to-MAC mapping changes.
- Monitoring TLS certificates and validating certificate chains and trust relationships.
- Analyzing DNS queries for suspicious redirection patterns.
- Using Intrusion Detection and Prevention Systems (IDS/IPS) and network traffic analysis.
- Identifying unauthorized or suspicious wireless access points.
- Analyzing authentication and session logs for unusual behavior.
A single indicator should not automatically be considered conclusive evidence of an attack, as some anomalies may result from legitimate network operations or configuration changes.
How Can Networks and Systems Be Protected Against MITM?
Effective protection begins with a Defense-in-Depth security strategy.
At the network level, organizations can implement Dynamic ARP Inspection, DHCP Snooping, network segmentation, and access control mechanisms according to their infrastructure requirements.
At the application level, organizations should enforce HTTPS, enable HSTS where appropriate, validate TLS certificates rigorously, and protect cookies with suitable security attributes such as Secure, HttpOnly, and SameSite.
At the identity level, phishing-resistant authentication, strong session management, and behavioral monitoring help reduce the likelihood of account compromise.
User awareness is equally important. Users should never ignore certificate warnings, should avoid suspicious wireless networks, and should not install untrusted certificates or applications.
The Role of Zero Trust in Preventing MITM Attacks
The Zero Trust security model reduces reliance on a device's network location as proof of trustworthiness.
It emphasizes continuous verification of identities, device security posture, access policies, and secure communication between systems.
When combined with encryption, identity management, and security monitoring, Zero Trust principles can reduce opportunities to exploit untrusted communications and limit the potential impact of security breaches.
Conclusion
Man-in-the-Middle attacks remain an important threat to digital communication security, particularly when combined with weak network configurations, inadequate authentication controls, or improper certificate validation.
As encryption protocols and browser protections continue to evolve, many traditional MITM attacks have become more difficult to execute. Nevertheless, organizations must continue monitoring communications and securing their networks, applications, and endpoints.
True cybersecurity is not solely about encrypting data in transit. It is about verifying the identities of communicating parties, maintaining the integrity of communication channels, and preventing unauthorized manipulation of information throughout its lifecycle.
Eng. Suhib Jarrah
Principal Cyber Security Engineer
Official Website: https://suhibjarrah.com
LinkedIn: Eng. Suhib Jarrah on LinkedIn